Thousands of credit cards stolen in Green Bay Packers store breach: American football team Green Bay Packers recently notified fans of a cybersecurity breach involving their official online store, Packers Pro Shop. In October 2024, malicious actors hacked the website, embedding a card skimmer script designed to steal sensitive customer information, including payment details.
Timeline of the Incident
According to a statement from Chrysta Jorgensen, Director of Retail Operations for the Packers, the breach was discovered on October 23, 2024. Upon learning about the intrusion, the team took immediate action by disabling all payment and checkout functionalities on the website, packersproshop.com, to prevent further unauthorized data access.
“On October 23, 2024, we were alerted to the presence of malicious code inserted on the Pro Shop website by a third-party threat actor,” Jorgensen shared in breach notification letters sent to affected customers. “Immediately upon learning this, we temporarily disabled all payment and checkout capabilities on the Pro Shop website and began an investigation.”
Investigative Measures
The Packers collaborated with external cybersecurity experts to assess the extent of the breach and identify the compromised data. The investigation revealed that the card skimmer script was active on the checkout page between late September and late October 2024. While the malicious code targeted personal and payment information, transactions made using gift cards, Pro Shop accounts, PayPal, or Amazon Pay were not affected.
The organization also took swift remedial actions, including:
- Removing the malicious code from the website’s checkout page.
- Refreshing all passwords related to the site’s management.
- Ensuring the hosting vendor addressed any remaining vulnerabilities.
Nature of the Breach
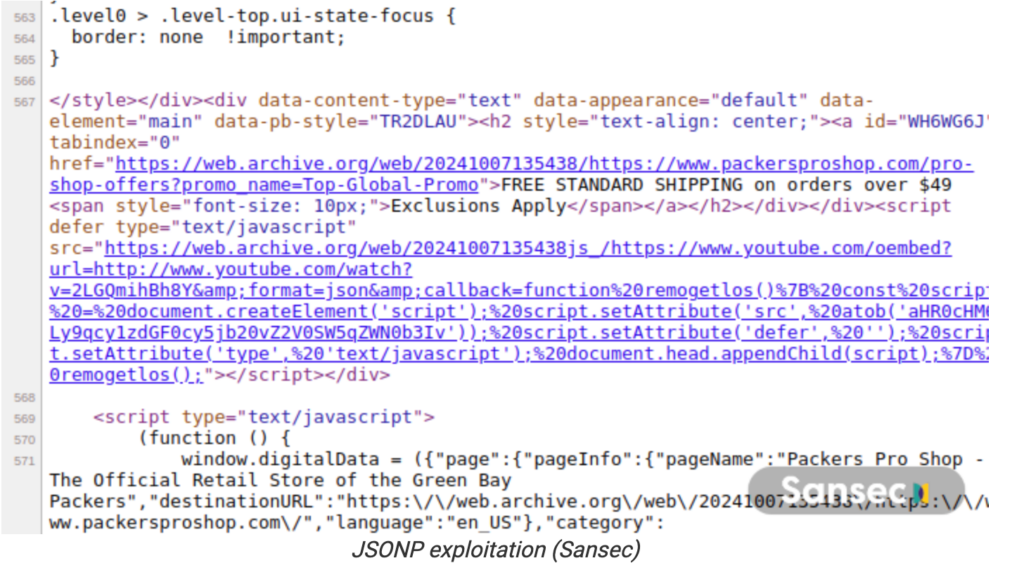
Dutch e-commerce security firm Sansec, which first alerted the Packers to the breach, reported that the attack leveraged a JSONP callback and YouTube’s oEmbed feature to bypass the website’s Content Security Policy (CSP). The malicious script, sourced from https://js-stats.com/getInjector, harvested data from various input fields and exfiltrated it to https://js-stats.com/fetchData.
The information compromised during this breach includes:
- Customer names
- Billing and shipping addresses
- Email addresses
- Credit card details (card type, number, expiration date, and CVV).
Post-Breach Actions
While the Packers have not disclosed the total number of affected customers, they have taken steps to mitigate the impact on those impacted. They are offering three years of complimentary credit monitoring and identity theft restoration services through Experian. Additionally, the team advises affected individuals to monitor their financial statements for any signs of fraudulent activity.
Guidance for Customers
The Packers urge customers who notice suspicious activity to take immediate action by:
- Reporting any suspected identity theft or fraud to their bank.
- Notifying relevant authorities, including their state attorney general and the Federal Trade Commission (FTC).
Industry Implications
This incident underscores the importance of robust cybersecurity measures PCI Compliance for e-commerce platforms. Leveraging expert insights and proactive monitoring can help prevent similar breaches in the future.
How To Protect Your Website from eSkimming Attacks
Payment Card Industry (PCI) 6.4.3 and 11.6.1 becomes mandatory on March 31, 2025. PCI 4.0 emphasizes the need to protect your visitors at the browser, a critical step in preventing eSkimming attacks. For comprehensive guidance on implementing these protections, Connect With Us and learn more about protecting against eSkimming and meeting requirements.
Original article reference: The original article detailing this incident can be found at Bleeping Computer.
Where to Start with PCI Compliance? Identify Your PCI Scope! The first step you need to take before beginning your PCI compliance journey is determining your PCI Scope. Get started with your complimentary PCI Scope Wizard today! Click below to book a free session with an expert who will guide you through the process. This 15–30-minute session is designed to save you countless hours of frustration—sit back and let us handle the details!